SEO, 서버 설정, 보안 점검, 사기 사이트 식별, 다크 패턴과 허위 정보. SiteScouter의 진단 내용을 바탕으로, 공공기관과 공식 문서를 근거로 해설합니다.
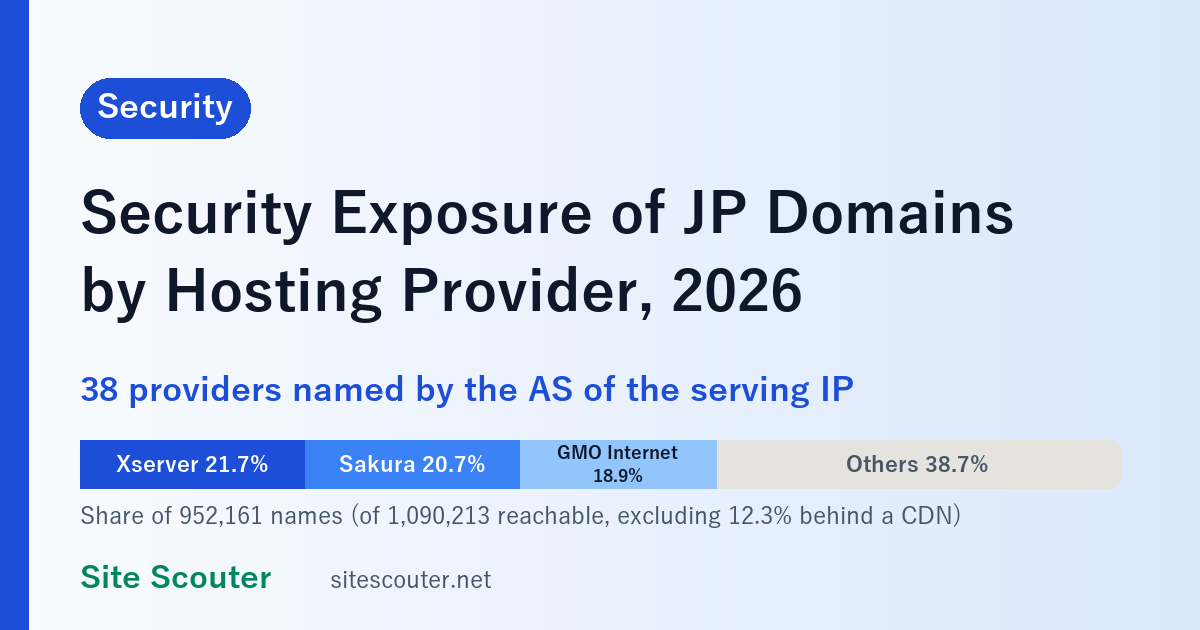
호스팅 사업자별 .jp 도메인 보안 실태. 응답 IP의 AS로 분류해 HSTS, CSP, TLS 1.3, PHP 지원 종료 비율을 비교했습니다.
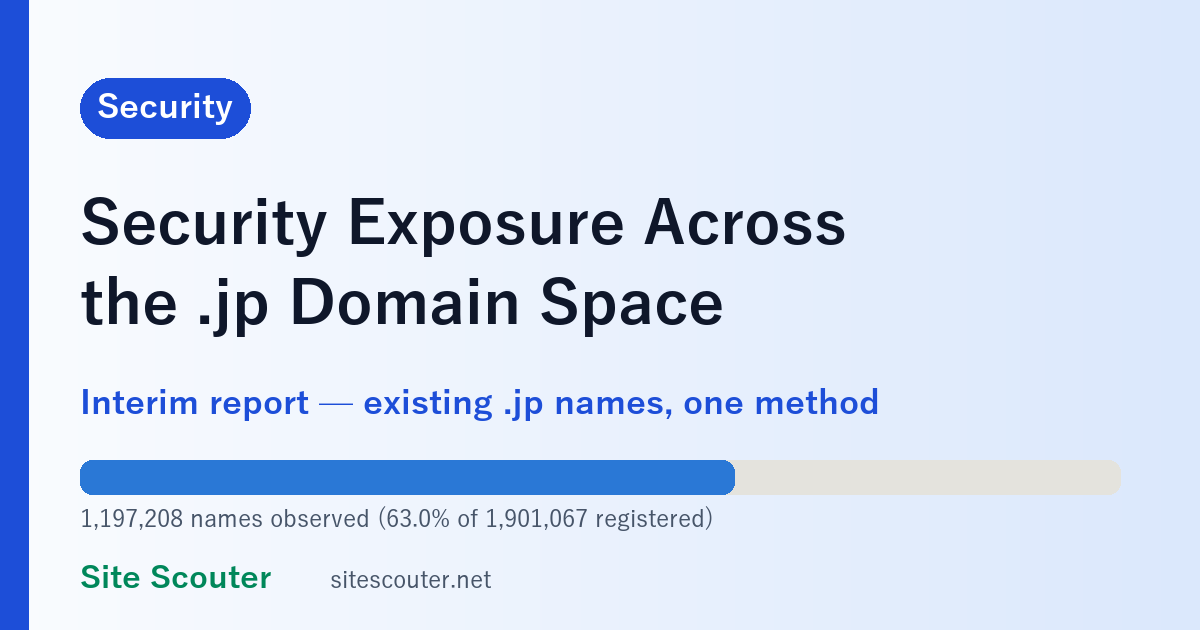
Interim report of a survey that applied one non-intrusive observation to every name in a ledger of delegated .jp domains (about 60% of the JPRS registration count): reachability with www fallback, HTTPS, HSTS and CSP, posture by domain type and DNS provider, TLS and certificates, PHP support status and the 2026 critical PHP vulnerabilities, CVE exposure (upper bound), WordPress plugins, SPF and DMARC, and a comparison with Japanese-language sites on gTLDs.
만화로 보는 SCS 평가 제도. 할아버지 공장이 ★3을 요구받았어요. 6화 18컷으로 공급망, 26가지 약속, 비용과 시간을 설명해요.
SCS 평가 제도 쉬운 해설. ★3을 요구받는 이유, ★3과 ★4의 차이, 절차, 비용(★3 연 ¥10,000), 2027년 3월 접수 일정.
SCS 공급망 보안 평가의 ★ 요구는 3차 협력사까지 내려갑니다. 경영진의 다섯 가지 결정과 실제 비용·기간을 정리합니다.
IPA SCS 공급망 보안 평가 핵심: ★3·★4 차이, CVSS 7.0 이상 14일 이내 패치, MFA, ★4 외부 진단 범위.
웹 보안 실태를 500만 사이트에서 관측한 최종 보고. HTTPS 강제 95.1%인데 HSTS 29.3%, CSP 16.6%에 그쳤습니다.
WHOIS상 GMO 사건 공격자 도메인은 10/28 03:35 JST 레지스트라가 clientHold 설정. 등록 기록과 도메인 업계의 견해.
웹 보안 조사 중간 보고. Common Crawl 100만 도메인을 추가하자 HSTS는 29.7%, CSP는 16.0%로 낮아졌습니다.
PHP 버전 업그레이드 방법을 확인, 전환, 동작 검증, 버전 숨기기 순서로 정리했습니다. CVSS 9.8 취약점의 수정 버전도 안내합니다.
Phone payment and bank websites have a "front door" that everyone sees, and an "inner door" you use when you log in. We knocked on 343 front doors and 1,010 inner doors. This manga gently shows which ones are stronger, and what can happen when a door is not strong.
For 341 payment and bank brand domains, I observed the security settings of the front host that everyone sees and of the "login-side hosts" that handle login and APIs with the same yardstick, and compared whether the two are aligned within the same brand. The indicator for which we can say that domains with a good front but a weaker login side outnumber the reverse was missing HSTS, at 5.1x. For the TLS version indicators, we could not say there was a difference (when one host per brand is picked at random).
결제·은행 사이트 보안 실태를 920곳에서 관측. 결제·은행의 26.4%에 HSTS 미적용·버전 노출 등의 미비점이 있었습니다.
A VPS service for automated FX trading went offline and its users were told to unplug their PCs. This article records the incident from public sources only, follows search suggestions and share prices, and sets out, in general terms, what under-investing in security can cost any operator (flash edition, updated every business day).
웹사이트 보안 조사 2026. 일본·G7 등 10개 지역 26.8만 사이트의 PHP 버전, HSTS, 취약점(CVE) 노출을 비교했습니다.
본 사이트에서는 서비스 제공 및 개선을 위해 쿠키를 사용하고 있습니다. 자세한 내용은 개인정보처리방침를 확인해 주세요.